Point of Trade Co.

Black Manta security emblem
Point of Trade Security · Black Manta

Black Manta. Built for the unseen.

Firewalls stop packets. Black Manta stops intent. It is our own protection layer, running above the firewall across Point of Trade’s network, reading behaviour, identity and intent rather than traffic alone.
First step live · the rest in detection mode
Point of Trade managed security: Black Manta watching over our datacenter network

We don’t block addresses. We block behaviour, and we know the difference between a scanner and an attacker.

Where it sits

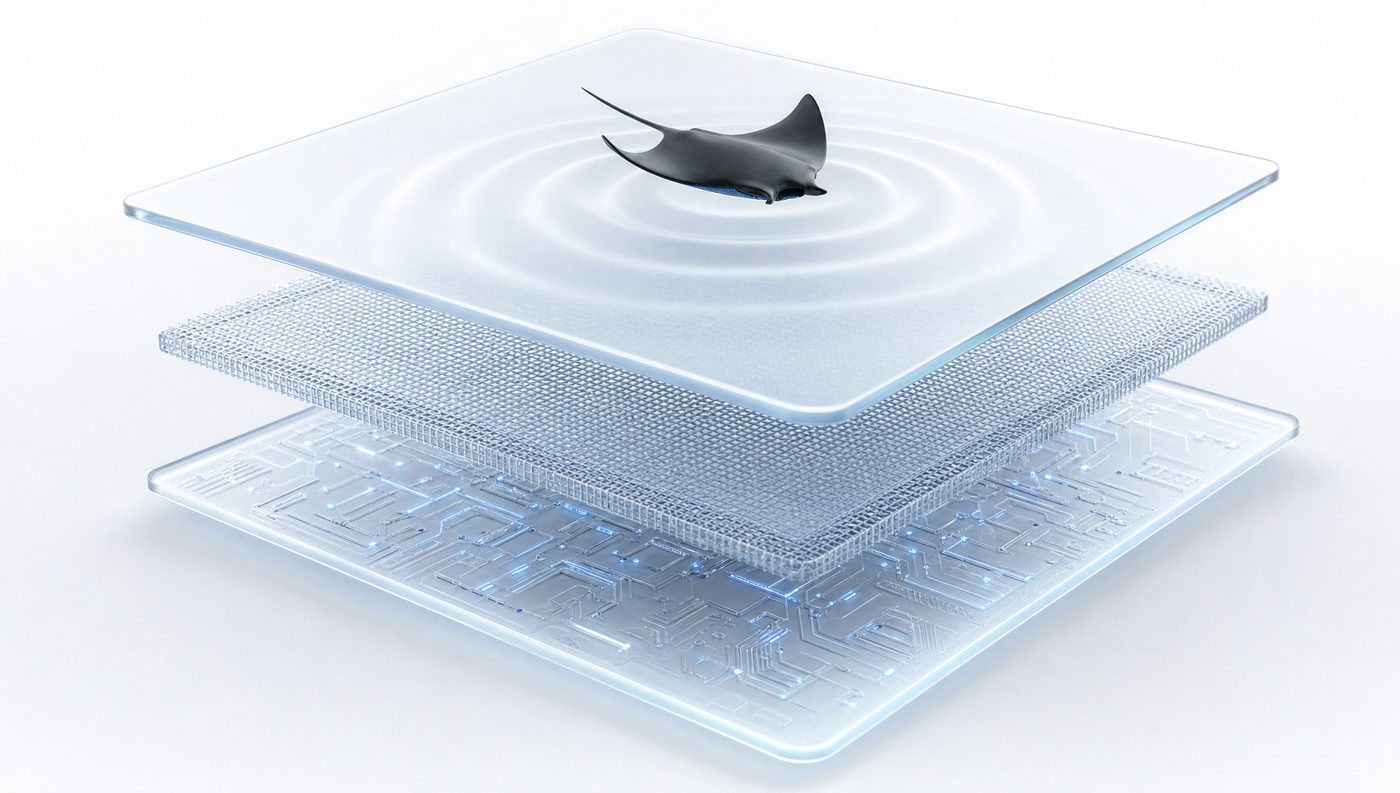
Managed security: the layer above the firewall

Black Manta does not replace the firewall. It reads what a firewall cannot: who is really connecting, what they are trying to do, and whether they have tried it before. It also shares its threat lists with our hardware firewall and reads back what the firewall sees. The firewall already blocks attackers caught probing our infrastructure across our whole network, customers’ cloud servers included, while the other lists stay in watch mode until each step is proven safe.

The internetEvery visitor, crawler, scanner and attacker
↓
Enterprise firewallPackets, ports and known-bad traffic
↓
Black MantaBehaviour, identity and intent
↓
Our infrastructure and your servicesOur network, the websites and mailboxes we host, and our platforms
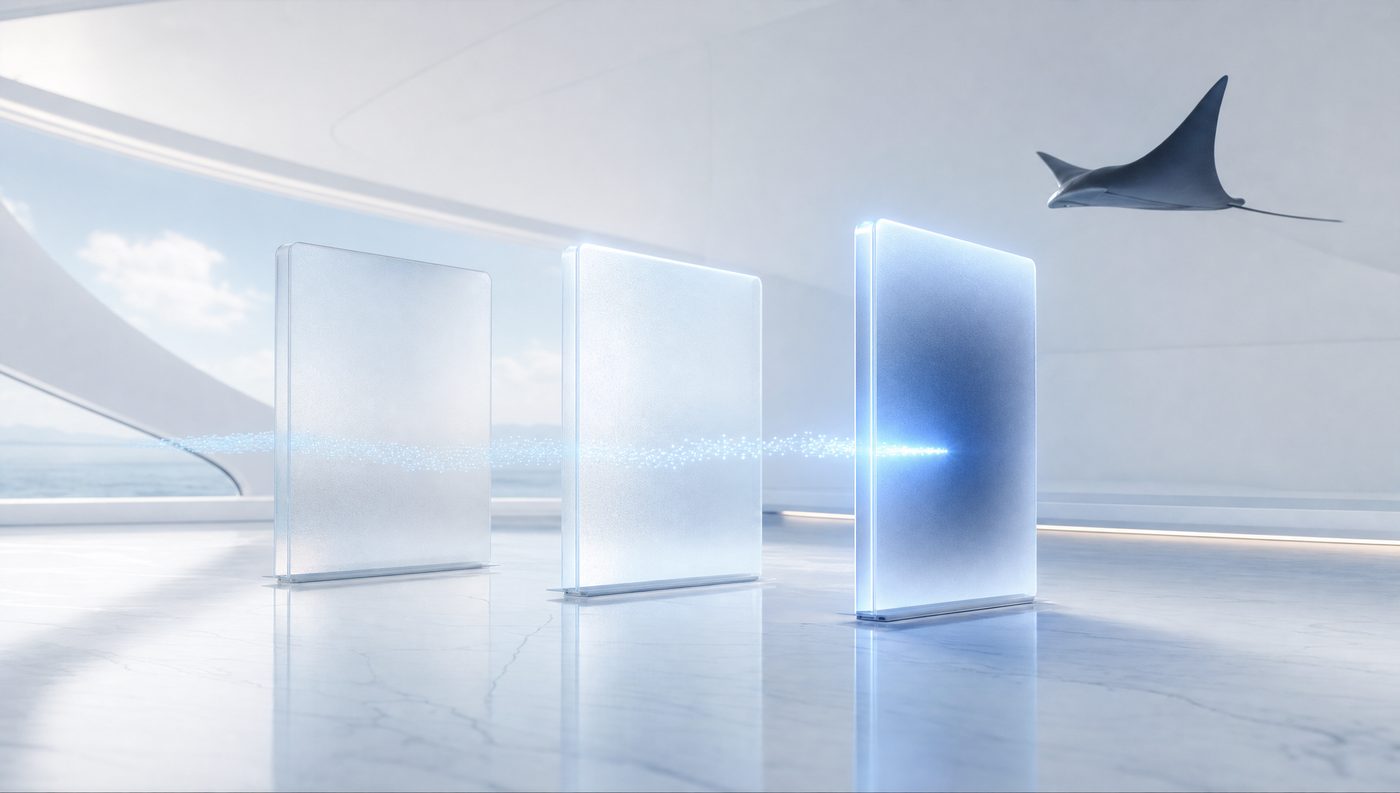
Point of Trade security layers: Black Manta sits above the firewall, shown as stacked glass layers
What it sees

Every attempt gets a name

More than a dozen detection families work together, each built on published intelligence rather than guesswork.

Identity before address

When a visitor claims to be Googlebot, Black Manta checks it against the address ranges Google publishes, not against its headers. The same check also applies to Bing, Apple and the major AI crawlers.

Every exploit, named

Black Manta names each attack attempt by CVE, then weighs it by whether the flaw is on CISA’s known-exploited list, whether ransomware crews use it, and how likely attackers are to exploit it (EPSS).

Attacks on AI assistants

Black Manta also detects attempts to manipulate our Zeta assistants in website chat and in the game panel, such as prompt injection, jailbreaks and data-leak tricks. It maps them to the 186 techniques of MITRE ATLAS and links attempts spread across many addresses into a single incident.

Web application attacks

Black Manta matches SQL injection, cross-site scripting, file inclusion, remote code execution and scanner probes with the OWASP Core Rule Set.

Credential attacks

Black Manta tracks credential stuffing, brute force and password spraying against the websites, mailboxes and hosting panel we run, and against SSH, together rather than one service at a time.

Compromised sites and servers

Black Manta matches links to malware hosted on sites we serve against public abuse data from abuse.ch, so we spot a compromised site from our side. On customer cloud servers it watches traffic in both directions: floods aimed at a server, and scanning, password guessing or spam from one that was hacked. It also tells a real service from an attack, so a stream serving its listeners is not mistaken for a flood. Sampled traffic also flags any of our servers that contacts a known botnet command server; Black Manta then lists that command server for the firewall, so we can cut the control line while the service keeps running.

Eyes on everything

An outside-in port sweep every six hours finds services nobody declared, and Black Manta reads our virtualisation platform and firewall policy every few minutes, so a new, renamed or removed server shows up within minutes. Even our edge router and name servers are watched: every configuration change is recorded with who made it, and a DNS zone that stops loading raises an alarm within minutes. We also check hosted WordPress sites daily against more than 48,000 vulnerable plugin and theme version ranges, and for exposed AI API keys.

Security identity checks: a scanning beam singling out one request among many
Identity first

Pretending is not a strategy

Pretend to be Googlebot from a rented server and the ranges Google publishes will answer you, not your headers. Black Manta recognises and manages AI crawlers, assistants and agent tools, and never blocks them just for being AI: only abuse counts as an attack.

Likewise, it recognises and tags research scanners from published projects, and never escalates against them. Black Manta knows who is looking, and who is only pretending to look.
Two postures

One engine, two postures

Our infrastructure: defended. Our customers: protected.

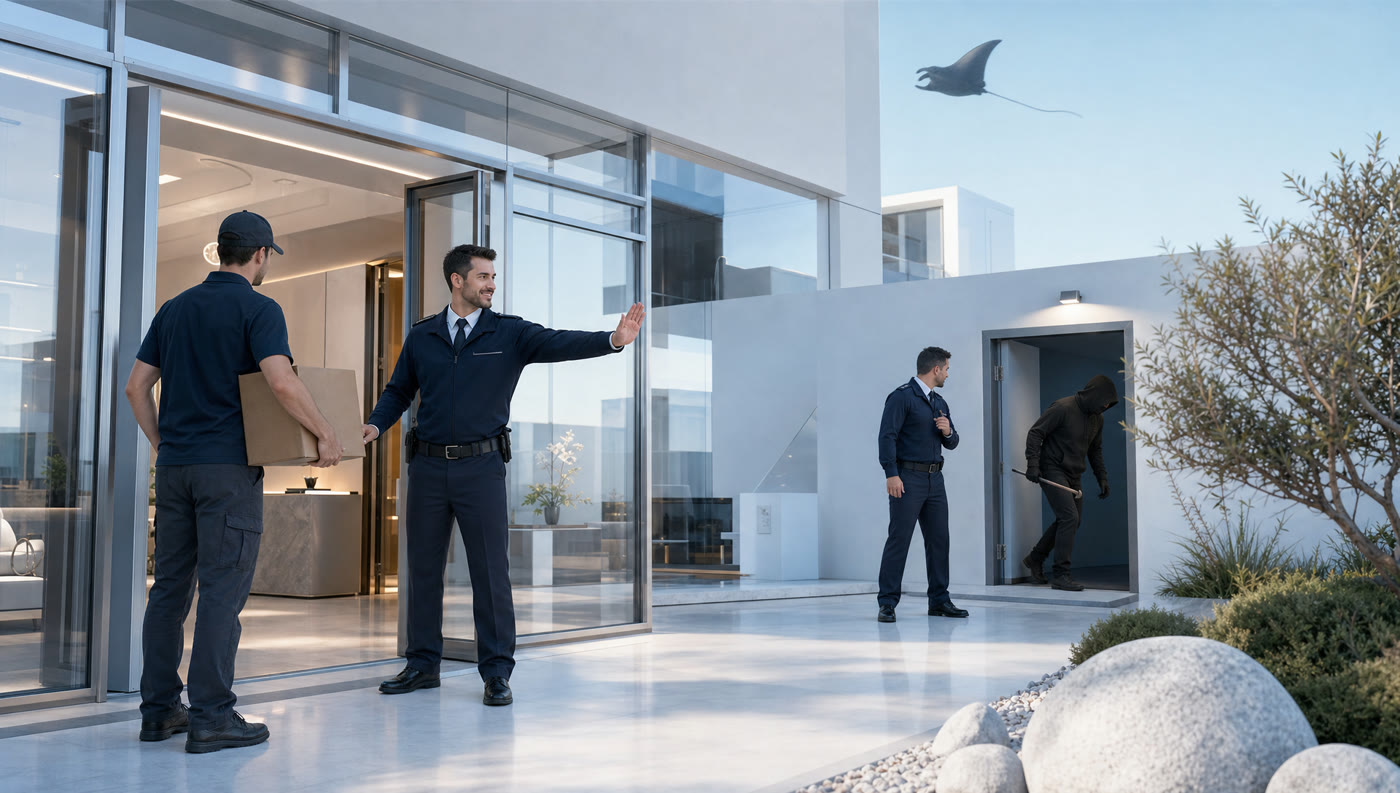
A security guard welcomes a courier in while a colleague catches an intruder sneaking out, the way Black Manta watches traffic in both directions
Infrastructure

Defended

On our own infrastructure Black Manta is strict. Suspicious behaviour climbs the response ladder quickly, because nothing there should be probing our systems.

Customer services

Protected

For the services our customers run, however, we built its rules to challenge before blocking, to require two independent signals before any block, and to notify before containing anything.

Game servers, VPN, live streams and remote desktops never pay a millisecond for any of this. That is because Black Manta watches them passively: it is not in their packet path.
Game servers

Every game server, watched on its own

Passive is not blind. Black Manta first learns each game’s normal traffic, so it can tell a busy evening from an attack. Automatic protection follows once each step is proven safe. You see its status on the server’s Black Manta card in the Game Panel and client area.
Floods and query-port abuse
Admin and join-password guessing
Bot join waves
Harmful mod files
Crash loops and servers that stop answering
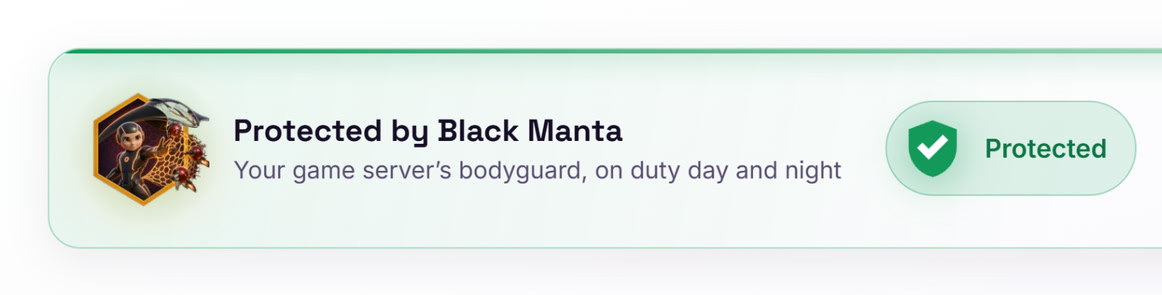
Real Game Panel screenshot: the Protected by Black Manta card on one of our test servers
The real card in the Game Panel, on one of our test servers.

If Black Manta raises an alert on your server, ask Zeta from the card. It answers in plain Arabic or English, in four parts:

  1. What is happening
  2. What we already did
  3. What you need to do now
  4. What happens next
Response ladder

Nine measured steps, never one blunt one

Every response is proportionate: the lightest step that works, and the next one only when the evidence earns it.

Observe
Tag
Challenge
Throttle
Tarpit
Block
Contain
Quarantine
Route block

Black Manta doesn’t play games, and it doesn’t guess. The first step is live: attackers Black Manta catches probing our infrastructure are now blocked at the firewall across our whole network, customers’ cloud servers included. Everything else stays in detection mode until each step is proven safe.

The update brain

Nothing goes live unverified

Black Manta’s intelligence changes every day, so Black Manta checks every change before letting it act.

Managed security checks: a data stream passing three glass checkpoints, the last one approving, as Black Manta grades every decision

Verified

Black Manta verifies every intelligence update at its source before using it.

Measured

If an update changes too much at once, Black Manta holds it back for review instead of applying it.

Protected

We protect verified crawlers, partners and our own ranges in code, so a bad feed cannot block them.

Recorded

We write every update to a ledger, so we always know what changed and when.

Rules grade every decision first, then an AI reviewer does, an independent AI judge rechecks those decisions every day, and our team has the final word. The engine also learns from its mistakes: on its own it can only become more careful, and becoming stricter takes our team’s approval. Finally, a kill switch returns everything to observe within minutes. Nobody has needed it.

39
Intelligence sources catalogued
6,500+
Exact attack signatures
150,000+
Malware and command-and-control indicators
582,000
Network ranges mapped to their owners
1,739
Known-exploited vulnerabilities tracked
186
AI-attack techniques mapped (MITRE ATLAS)
29,700
Research-scanner ranges recognised
5min
Live service map refresh

Figures as of October 2026. Intelligence includes CISA KEV, FIRST EPSS, MITRE ATLAS, the OWASP Core Rule Set, ProjectDiscovery nuclei templates, MISP warninglists and abuse.ch, among other published sources.

Questions

Straight answers

Does Black Manta replace the firewall?

No. It is a separate layer above our enterprise firewall. While the firewall handles packets and ports, Black Manta reads behaviour, identity and intent.

Will it slow down game servers or the VPN?

No. Game servers, VPN, live streaming and remote desktop are latency-sensitive, so Black Manta watches them passively. It is not in their packet path and adds no latency. Even so, it watches every game server on its own.

Does it block search engines or AI crawlers?

Black Manta protects verified crawlers in code: it checks their identity against the address ranges their operators publish. It also recognises and manages AI crawlers, assistants and agent tools, and does not block them for being AI.

Is Black Manta blocking attacks today?

Partly. The first step is live: the firewall now blocks attackers caught probing our infrastructure, across our whole network, customers’ cloud servers included. Everything else stays in detection mode until each step is proven safe.

Serious about what you run? So are we.

Talk to our team about the services you run with us and how Black Manta watches over them.